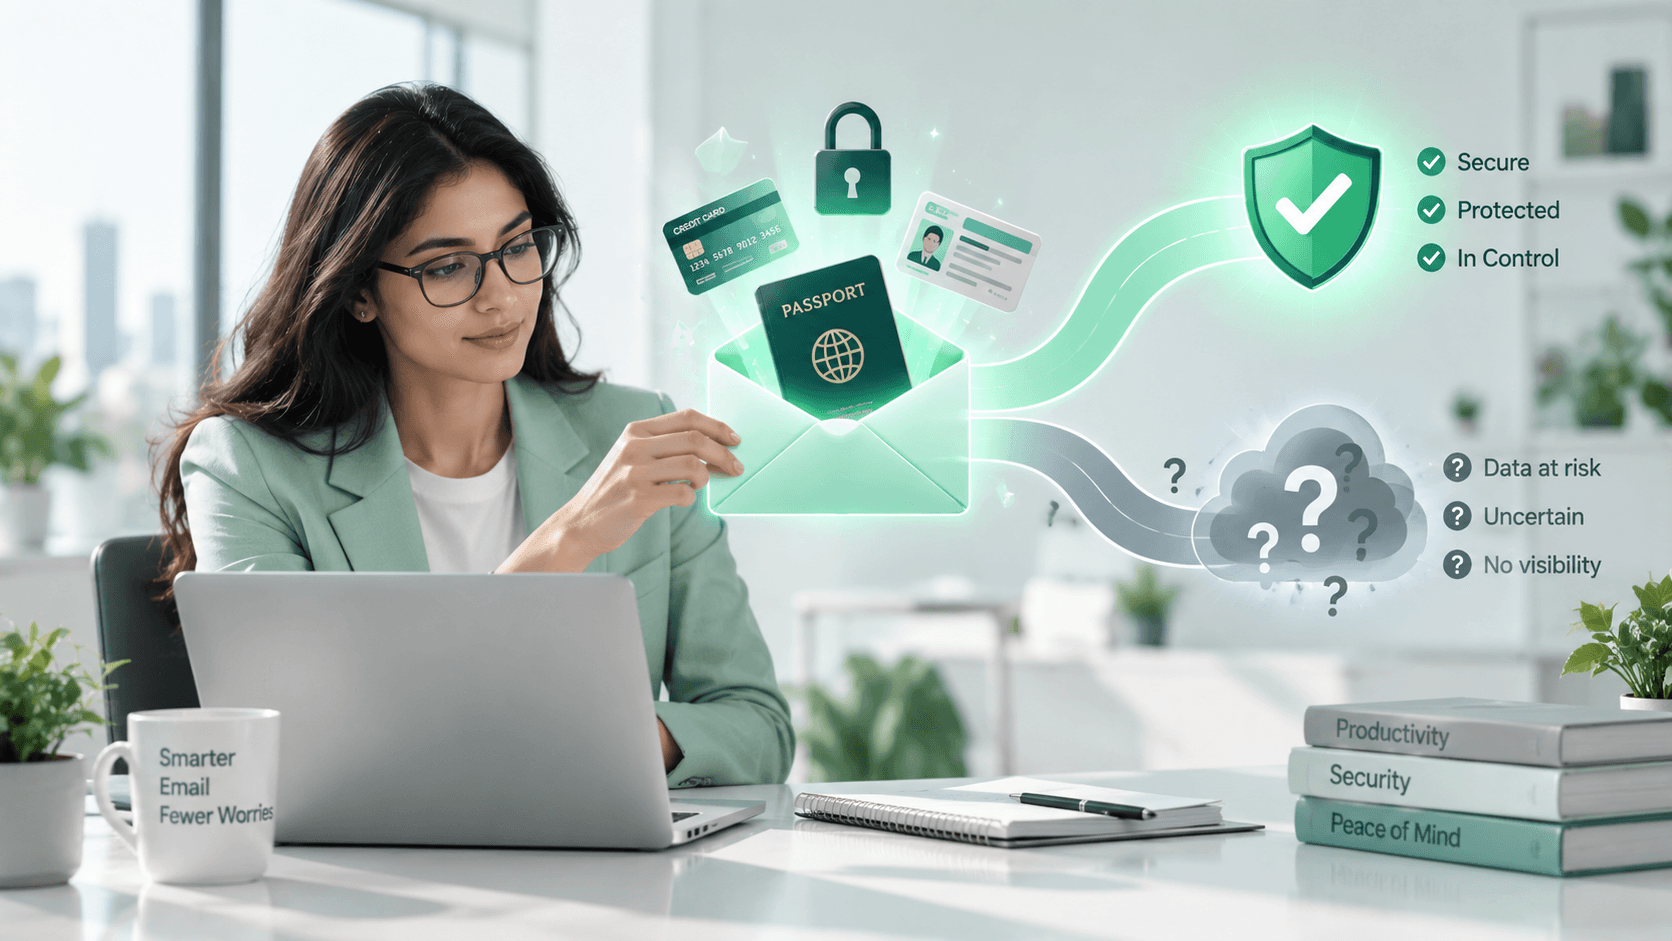
You connect an AI email tool to your inbox. You click through a permissions screen. The tool starts reading your messages, drafting replies, sorting your mail, and saving you time.
But your inbox isn't just conversations. It's years of accumulated communication containing client contracts, financial documents, passwords people shouldn't have emailed, medical appointment details, legal discussions, tax forms, and personal information that exists in email because nobody thought twice about hitting send.
The National Cybersecurity Alliance published guidance specifically addressing this, noting that most people don't realize how much personal data they share with AI tools or what happens to that data after it's processed. For email tools, the stakes are higher than for most AI applications because the data isn't something you chose to submit. It's your entire communication history, made available through a single authorization click.
The question most professionals skip before connecting: what actually happens to all of that once the AI can see it?
What access do AI email tools actually get when you connect them?
Full read access to your entire inbox, in most cases. Not just new messages. Everything.
Most AI email tools connect through OAuth 2.0, a standard authorization protocol where your email provider issues a scoped access token instead of sharing your actual password. Google and Microsoft both use this system. You see a permissions screen listing what the tool is requesting: read your emails, send on your behalf, manage your labels, access your contacts.
What that screen means in practice is that the tool can now read every email in your account. Your inbox, your sent folder, your archive, your drafts. Years of communication history, accessible through that one authorization.
The scope of permissions varies by tool. Some request read-only access, meaning they can see your email but can't send or modify anything. Others request full access including the ability to send messages from your account, which means the tool could compose and send an email as you without you writing it.
That distinction matters because it determines what happens if something goes wrong. A compromised tool with read access exposes your email history. A compromised tool with send access can impersonate you to your clients, partners, and contacts.
Security researchers recommend granting read-only access first and expanding permissions gradually. Most of the useful functionality in AI email tools comes from reading and drafting. Send permissions carry additional risk and should only be granted after the tool has been verified over time.
Google's own CASA (Cloud Application Security Assessment) program exists specifically to evaluate the security practices of applications requesting OAuth access to user data. The verification process examines how the application handles, stores, and protects the data it accesses. Not all AI email tools go through this assessment, and professionals should check whether the tool they're considering has been verified.
Does the AI tool store your email content?
This varies significantly between providers, and it's the question most professionals don't think to ask.
Some tools process your email in real time and don't retain the content after generating a response. The email goes in, the AI produces a summary or draft, and the original content is discarded from the tool's systems. Your data passes through but doesn't live there.
Others store your email content on their own servers. Sometimes to improve performance through caching. Sometimes for analytics about how the tool is being used. Sometimes explicitly for training their AI models. The retention periods can range from 30 days to multiple years.
The GDPR, which applies to any business handling data of EU residents regardless of where the business is located, requires documented justification for any data retention. Article 5 of the regulation establishes the principle of storage limitation: personal data should be kept only for as long as necessary for the purpose it was collected. An AI email tool that retains your inbox data indefinitely without a clear, documented purpose is potentially in violation of this principle for any user based in Europe.
For professionals in regulated industries, the retention question carries additional weight. HIPAA requires specific handling and retention policies for protected health information. If a healthcare professional's email contains patient data, and the AI tool stores that data on its own servers, the tool's infrastructure becomes subject to HIPAA requirements. The same logic applies to financial regulations, legal privilege protections, and industry-specific compliance frameworks.
The specific question to ask before connecting: does this tool store the content of my emails on its servers? If yes, for how long? Where? Who can access it? If the answer requires reading 40 pages of terms of service to find, that tells you something about how much the provider wants you to know.
Is your email data used to train AI models?
This is the question that should come before any feature comparison.
The difference between "processing" and "training" is fundamental. Processing means the AI reads your email to perform a task and then discards the content. Training means the AI incorporates patterns from your data into the model permanently, affecting how the system responds to every other user.
Published research in machine learning has demonstrated that large language models can memorize and reproduce specific data from their training sets. A 2023 paper from Google DeepMind researchers, titled "Extracting Training Data from Large Language Models," showed that models can be prompted to output verbatim text from their training data, including personally identifiable information. If your client's contract terms or financial details end up in a training dataset, there is a documented probability that fragments of that information could surface in the model's outputs to other users.
Some AI providers explicitly exclude customer data from model training. Others include it by default and offer an opt-out buried in account settings. The difference is not always obvious from the product's marketing materials.
The consumer versions of major AI platforms typically have more permissive data training policies than enterprise versions. Professionals who paste email content into free AI chat tools are often contributing to training datasets without realizing it, because the free tier's terms of service allow training use by default.
For any professional handling client data, financial information, legal communications, or health records, the training question is not optional. An AI tool that trains on your email data is not just reading your inbox to help you. It's learning from your inbox to help everyone else who uses the same model.
This is also why the distinction between using a dedicated AI email tool versus pasting emails into a general-purpose AI chat matters. When you paste an email thread into a chat interface, you're manually submitting that content. It leaves your email system entirely and enters a different platform with its own data retention and training policies. The content is no longer protected by whatever security your email provider offers. It lives wherever the chat platform stores it, under whatever terms the chat platform operates.
A dedicated AI email tool that connects through OAuth and processes data within a controlled pipeline is a different architecture. The email content may never leave the provider's processing environment, depending on the tool. But the key word is "may." The architecture is only as trustworthy as the provider's actual implementation, which is why the privacy policy matters more than the marketing page.
What sensitive information is actually sitting in your inbox?
More than most professionals actively track. Your inbox is not a curated dataset you chose to share. It's an unfiltered accumulation of everything anyone has ever sent you, plus everything you've sent in return.
Client financial information. Bank account numbers, tax identification numbers, income details, investment positions, wire transfer instructions. Professionals in accounting, real estate, legal, and financial services receive these as routine parts of their work, often as unencrypted email attachments.
Legal communications. For attorneys, every email exchange with a client is potentially covered by attorney-client privilege. When an AI tool reads those emails, a third party is accessing privileged communications. The American Bar Association has published guidance on attorneys' ethical obligations regarding technology and client data, emphasizing the duty to make reasonable efforts to prevent unauthorized disclosure.
Medical and health information. Appointment confirmations, insurance details, prescription information, referral notes, test results. Healthcare professionals handle this under HIPAA. But anyone with medical information in their personal email has health data sitting in an inbox that an AI tool can now read.
Personal identification documents. Social Security numbers, passport copies, driver's license images, visa paperwork, immigration documents. International professionals handling applications and renewals have some of the most sensitive personal data imaginable flowing through their accounts.
Credentials and access information. Despite decades of security guidance, people still email passwords, API keys, login credentials, two-factor backup codes, and shared account access details. These sit in the inbox alongside everything else, fully accessible to any tool with read permission.
Internal business data. Revenue numbers, hiring plans, product strategy, investor updates, board materials, partnership negotiations. A founder's inbox contains the entire strategic picture of their company.
When you authorize an AI email tool, you're giving it access to all of this at once. The tool doesn't distinguish between a lunch invitation and a wire transfer confirmation. It reads everything it has permission to read, which after OAuth authorization is everything.
What should professionals actually check before connecting an AI email tool?
Five things. In this order.
What permissions does the tool request? Read the OAuth scope screen carefully. Read-only access to email is the safest starting point. Send capability, contact access, calendar access, and file storage access each add risk. Grant only what the tool needs to function and nothing more.
Does the tool store your email content? If yes, on whose servers, in what country, for how long, and under what security protections? A tool that processes in real time and discards is fundamentally different from one that copies your inbox to its own infrastructure. If you're in a regulated industry, your compliance obligations extend to wherever your data is stored.
Is your data used for model training? Read the privacy policy specifically for language about improving AI models, enhancing services, or similar phrasing that indicates training use. Check whether training is opt-in or opt-out. If it's opt-out, verify that the opt-out actually works and isn't just a preference that gets overridden during model updates.
Has the tool been independently verified? Programs like Google's CASA assessment evaluate how applications handle OAuth access to user data. SOC 2 certification evaluates security controls and data handling practices. An AI email tool that has gone through independent security verification is demonstrably different from one that asks you to trust its marketing claims.
What happens to your data if you stop using the tool? Is the data deleted when you disconnect? How quickly? Can you request deletion? Some providers retain data after account termination, citing backup requirements. You should know the answer before connecting.
Where regulations are heading
The EU AI Act, applicable since August 2025, classifies certain AI systems handling sensitive data as "high-risk," triggering requirements for risk assessment, data quality controls, comprehensive logging, human oversight, and detailed documentation. Some email AI applications fall into this category depending on how they process personal data.
The GDPR continues to evolve in its application to AI. European data protection authorities have examined whether AI models trained on personal data are themselves subject to GDPR provisions, with initial guidance suggesting they are in most cases because of memorization capabilities.
In the United States, state-level privacy laws in California (CCPA/CPRA), Virginia, Colorado, Connecticut, and others establish consumer rights over personal data including the right to know what data is collected, the right to delete it, and the right to opt out of its sale or use for certain purposes.
The regulatory direction globally is toward more transparency, more consent requirements, and more restrictions on how AI providers handle personal data. Tools that operate under permissive data practices today may face compliance issues as regulations tighten. Professionals who choose an AI email tool based only on features risk finding themselves on the wrong side of a compliance requirement that didn't exist when they signed up.
The practical implication is that data practices aren't just a privacy consideration today. They're a future-proofing decision. A tool that handles data responsibly now, with clear processing boundaries, no training on customer data, and transparent retention policies, is a tool that won't create compliance problems when new regulations arrive. A tool with loose data practices is a liability that grows more expensive to unwind with every month of accumulated data.
For professionals who handle sensitive client information across real estate, legal, healthcare, financial services, or consulting, the AI email tool they choose today will be processing years of sensitive communications within months. The data practices of that tool are as important as its features, and they're harder to change after the fact.
The question that should come first
Most professionals evaluate AI email tools by asking what the tool can do. Can it draft replies? Can it summarize threads? Can it categorize my inbox? Those questions determine how useful the tool is.
The question that should come before all of them: what does the tool do with what it sees?
An AI email tool that processes and forgets is a productivity tool. An AI tool that stores and trains is a data liability dressed up as a productivity tool. A tool with read-only access has a contained risk profile. A tool with full send access is a completely different conversation.
The features determine how much time you save. The data practices determine how much risk you take on. Both matter. But only one of them is visible on the product page, and only one of them shows up after something goes wrong.
Your inbox is the most complete record of your professional life. Every client relationship, every deal negotiation, every sensitive document, every personal detail anyone has ever sent you. The decision to give an AI tool access to all of that deserves more than a quick click through a permissions screen.
SmartMail was built with this reality at the center. You get to use AI and AI agents to draft, summarize, categorize, and act on your emails while your sensitive data and credentials always remain safe from the AI itself. Multilayered protection runs before AI processes any email content, so the things that should never reach a model don't reach it. Your data isn't used for training. SmartMail has completed Google's CASA security verification. The protections aren't an afterthought bolted on after the features were built. They're the foundation everything else runs on.
Related Posts